PROMPT SKETCH
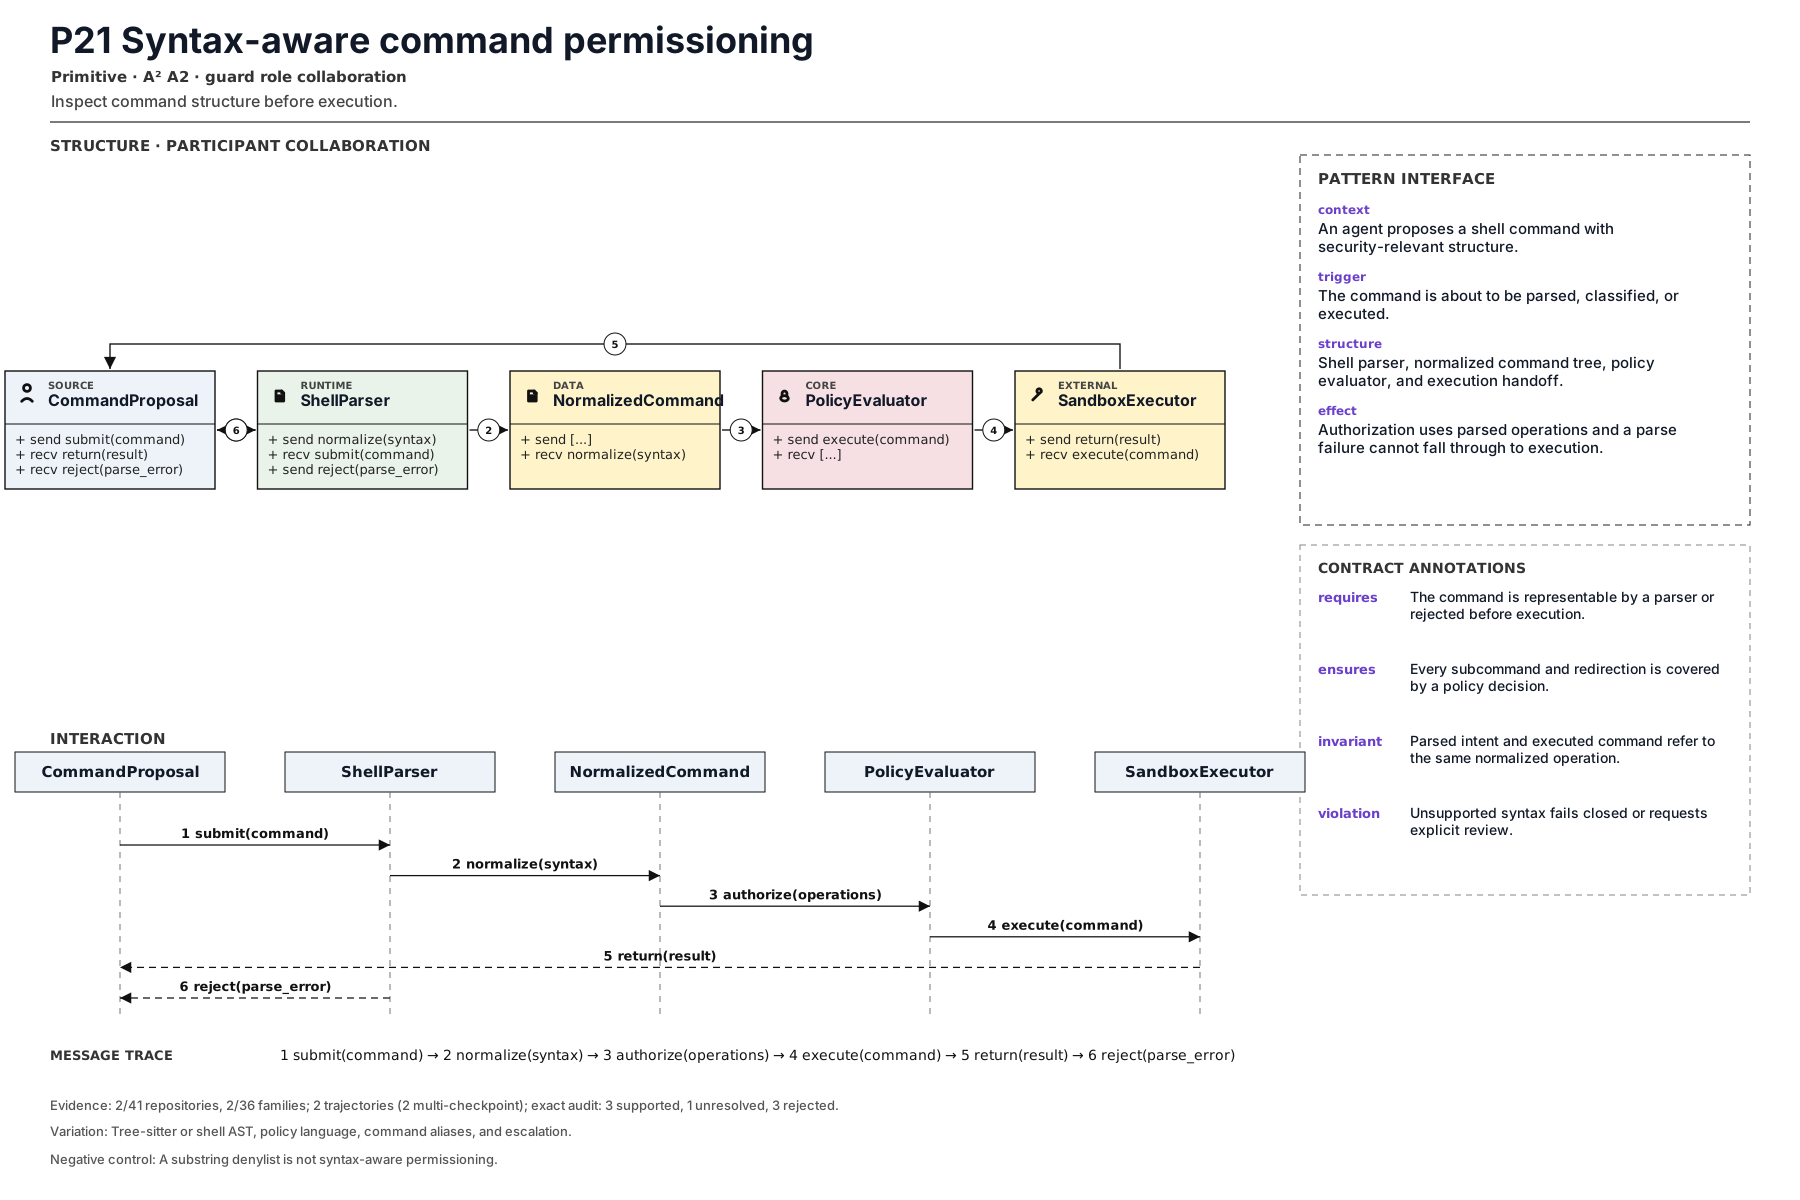
Parse shell commands before execution. Every subcommand, pipeline stage, and redirection must receive a policy decision; if the command cannot be parsed, reject it rather than guessing.Inspect command structure before execution.
command_authorization_boundaryRECORD STATUSCandidate · v0.1.0The proposed contract drawn as participant roles, received calls, and numbered dependencies.
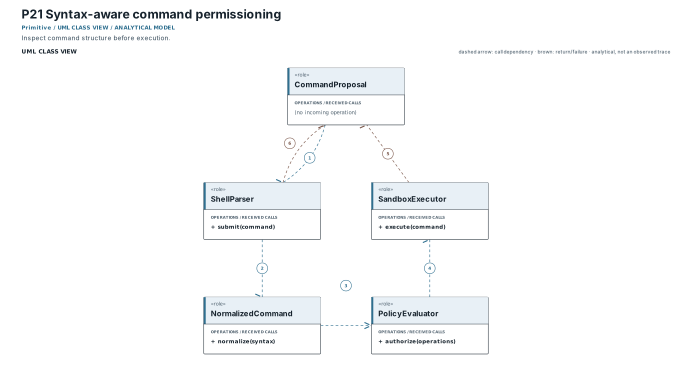
The same roles and calls as a class collaboration and a numbered message sequence.
Where the mechanism applies. All four dimensions belong to the proposed match, not just its vocabulary.
The obligation that clients, operators, and auditors should be able to rely on.
A substring denylist is not syntax-aware permissioning.
The hot spot is admitted only where the protected semantics survive.
Tree-sitter or shell AST, policy language, command aliases, and escalation.
Test pipes, substitutions, quoting, malformed input, and policy bypass attempts.
Did policy move from string matching to parsed operation boundaries?
An illustrative prompt and a small design sketch for the proposed contract. Names and APIs are invented; this is not a repository excerpt.
Parse shell commands before execution. Every subcommand, pipeline stage, and redirection must receive a policy decision; if the command cannot be parsed, reject it rather than guessing.def authorize(command, policy):
try:
tree = shell_parser.parse(command)
except ParseError:
return Decision.deny("unparseable command")
decisions = [policy.decide(node) for node in walk(tree)]
if any(decision.denied for decision in decisions):
return Decision.deny(decisions)
return Decision.allow(decisions)Illustrative design sketch. String matching on the full command cannot cover every nested effect. This example is a teaching aid, not implementation evidence or a conformance claim.
The frozen rule that retrieves this record, the canonical source exemplar, and the control that should stay unmatched.
command_authorization_boundary(?i)\b(?:shell[_-]?pars|command[_-]?pars|bash[_-]?pars|syntax[_-]?aware|authorize[_-]?command)\bFrozen expression, v0.1.0. A match is a retrieval cue, not a confirmed implementation.openhands-sdk/openhands/sdk/security/shell_parser.py:58Support: tests/sdk/security/test_shell_parser.py:1Scope-anchored review. pohe-agent analyze <repo> --pattern P21 anchors the cue to its enclosing declaration and checks a separate operational signature for all four pointcut dimensions. Missing roles and negative-control risks remain visible; a structural match is not E2/E3. Calibration report ↗
Up to five public files retrieved by the frozen cue and pinned to the audited commit. A match is a place to inspect, not a confirmed implementation.
Each layer answers a different question. Do not substitute retrieval for review.
A concrete source anchor is available for this proposed record. It is one exemplar, not evidence that all repositories—or every contract field—conform.
Review boundary: this candidate and its specification come from an AI-assisted study. Independent human validation remains open.
5.6% of repository families in the frozen panel have at least one current cue, historical cue, or canonical source layer. This is not confirmed prevalence.
Current lexical-cue repositories: 1 / 415c524ad65d81openhands-sdk/openhands/sdk/security/shell_parser.py:58tests/sdk/security/test_shell_parser.py:1Tree-sitter shell parse before policy evaluation.
(?i)\b(?:shell[_-]?pars|command[_-]?pars|bash[_-]?pars|syntax[_-]?aware|authorize[_-]?command)\bThis expression is a discovery instrument only. A match is a retrieval cue—not a confirmed implementation, pointcut match, or contract proof.